Microsoft Defender for Cloud
Cloud security posture management and workload protection for Azure, AWS, GCP and hybrid environments.
Technical Overview
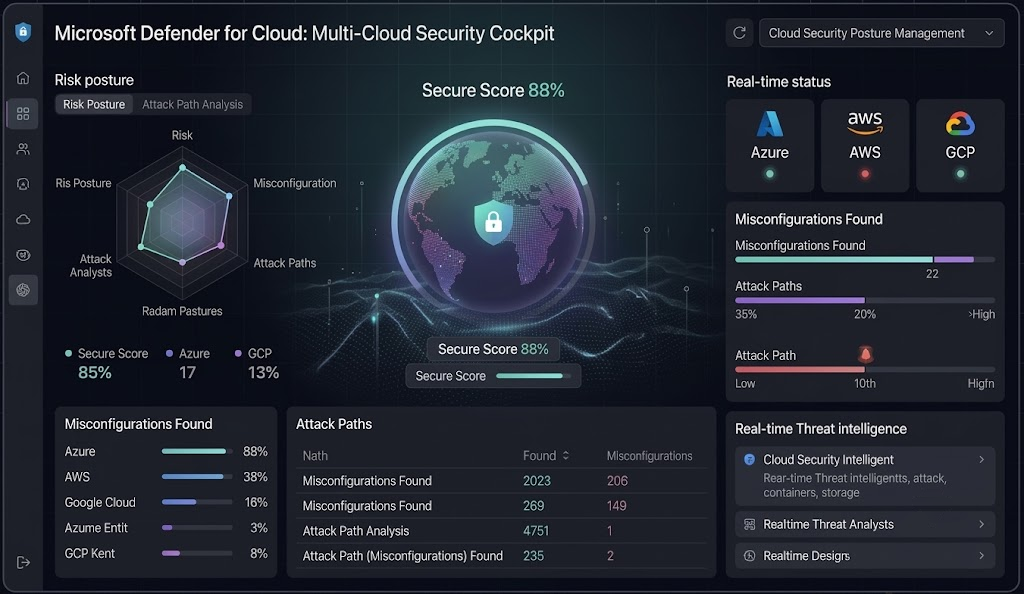
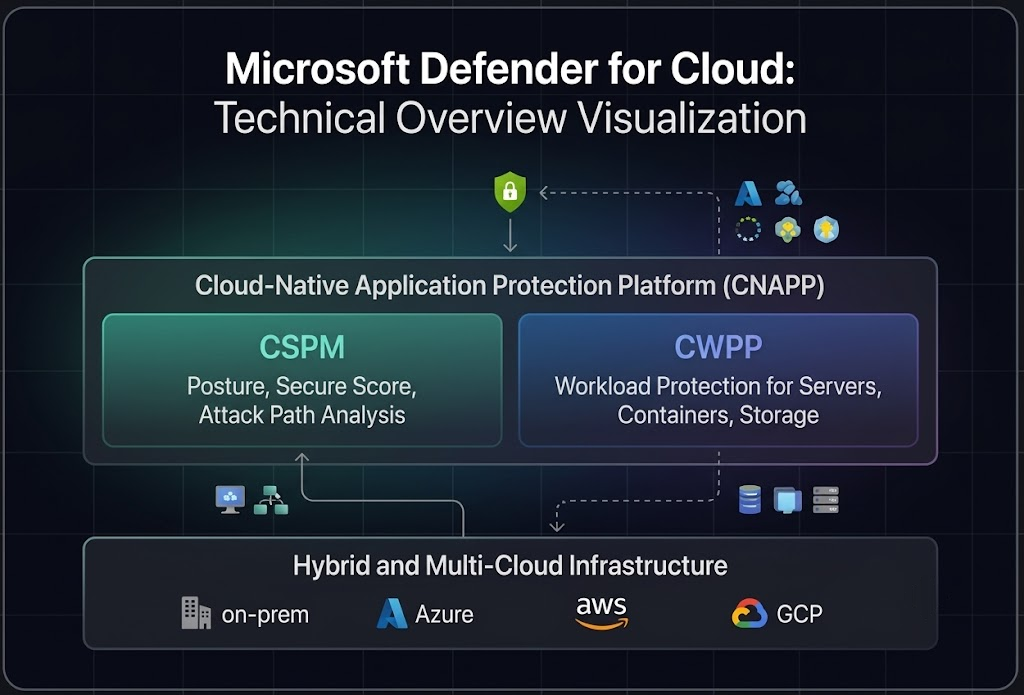
Microsoft Defender for Cloud is a cloud-native application protection platform (CNAPP) that provides security posture management and workload protection for Azure, AWS, Google Cloud and hybrid environments.
It combines CSPM (posture, secure score, recommendations, attack path analysis) with CWP plans for servers, containers, storage, databases, App Service, Key Vault and APIs.
How Microsoft Defender for Cloud works
A five-step technical flow.
Technical architecture
Operating flow of Microsoft Defender for Cloud from onboarding to outcome.
- 01Connect environmentsOnboard Azure subscriptions and AWS/GCP accounts.
- 02Assess postureBenchmarks produce recommendations and secure score.
- 03Prioritise riskAttack paths and the security graph rank exposure.
- 04Protect workloadsDefender plans detect threats and vulnerabilities.
- 05RespondAlerts flow to Defender XDR, Sentinel and workflows.
Connect environments → Assess posture → Prioritise risk → Protect workloads → Respond
Core Capabilities
Defender for Cloud offers continuous posture assessment against Microsoft cloud security benchmark and regulatory standards, attack path and cloud security graph analysis, vulnerability assessment, just-in-time VM access, adaptive controls, DevOps security for code repositories and pipelines, and threat detection alerts per workload.
Integrations
Defender for Cloud integrates with Microsoft Defender XDR, Microsoft Sentinel, Azure Policy, Azure Arc for hybrid servers, Defender for Endpoint on servers, and GitHub and Azure DevOps. Alerts and recommendations can be exported through APIs, Event Hub and Logic Apps.
Key benefits
Main outcomes you can expect.
- 01Multicloud VisibilityOne posture view across cloud platforms.
- 02Risk PrioritisationFix the paths attackers can use first.
- 03Workload ProtectionThreat detection for servers, data and containers.
- 04Compliance TrackingMap posture to regulatory standards.
Implementation Approach
We inventory subscriptions and accounts, enable foundational CSPM, onboard AWS/GCP connectors and Arc-enabled servers, and choose Defender plans by workload risk. Recommendations are prioritised and remediated with owners, alerts are integrated with your SOC, and governance rules track progress.
Operational & Security Considerations
Defender plans are billed per resource, so scope them deliberately. Use least-privilege roles for connectors, test auto-remediation and Azure Policy enforcement in non-production first, and confirm plan availability and current pricing.
How ISS Technologies Helps
ISS Technologies assesses your environment, implements and integrates Microsoft Defender for Cloud, and supports your team in day-to-day operations. Related service: Managed SOC.